Blog
Cyber Security
The TARA Arrives, Its References Don't
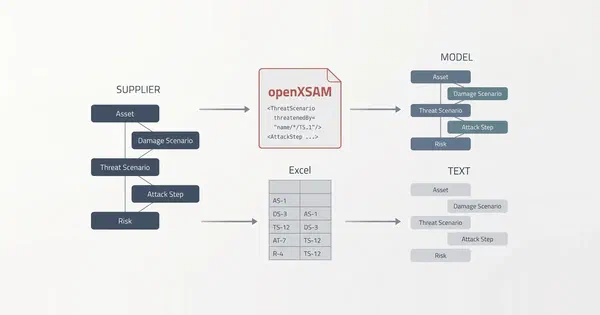
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article Jens Bühl
8 min read
Holistic protection and seamless traceability for cybersecurity, functional safety, and the Cyber Resilience Act
Overview

Methodological excellence and tailored tools for model-based system and software engineering.
Overview

Enterprise software from a single source: AI integration, legacy migration and full-stack development — cost-efficiently and sovereignly hosted.
Overview

Every insight with a product reference at a glance — filterable by itemis ANALYZE, itemis CREATE and itemis SECURE.
Product
Format
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article
Jens Bühl
8 min read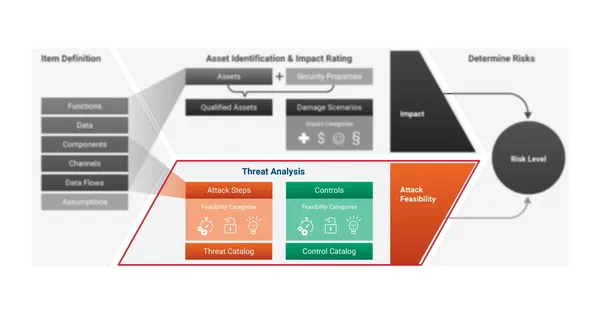
Threat scenario, attack path and attack feasibility belong together: what makes a scenario, why the path gets rated, and how the method shifts the result.
Read Article
Jens Bühl
13 min read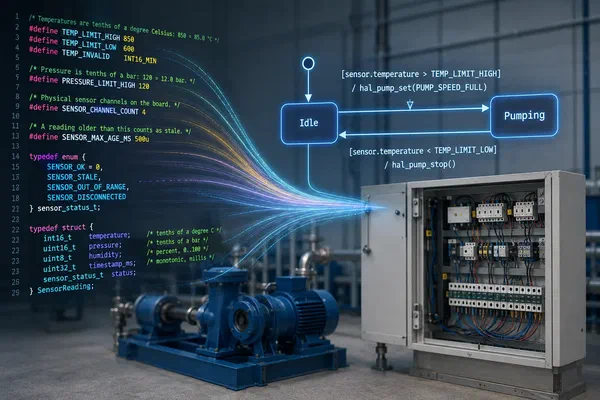
The statechart sketch gets implemented by hand, and then the two drift apart. How itemis CREATE pulls existing C, C++ and Java code straight into the model.
Read Article Axel Terfloth
10 min read
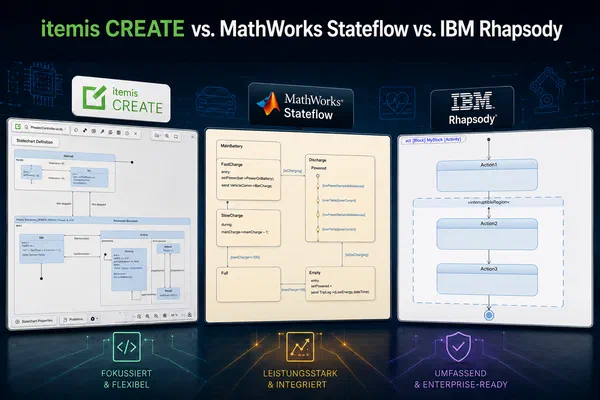
An honest, detailed comparison of three leading statechart tools — MathWorks Stateflow, IBM Rhapsody, and itemis CREATE — covering features, pricing, and which tool fits which team.
Read Article
Axel Terfloth
8 min read
Six guardrails for AI agents in ASPICE assessments: scripts over prompts, persisted results and progress, batching, closed questions, prohibitions, flagging.
Read Article Pierre Dammé
6 min read
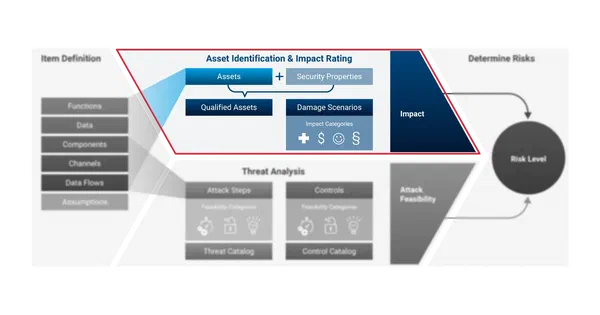
Asset identification and impact rating supply one half of the risk value: when an element of the item becomes an asset, whose damage a damage scenario describes, why the safety rating is not security's to set alone, and what keeps ratings comparable across projects.
Read Article
Jens Bühl
15 min read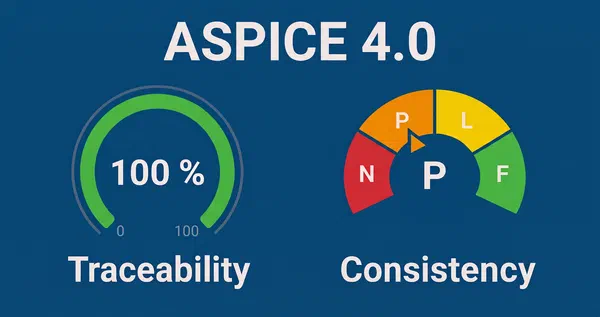
100% link coverage does not mean ASPICE compliance. How a type check, a consistency check and a consistency score expose semantic inconsistencies with LLMs.
Read Article
Pierre Dammé
7 min read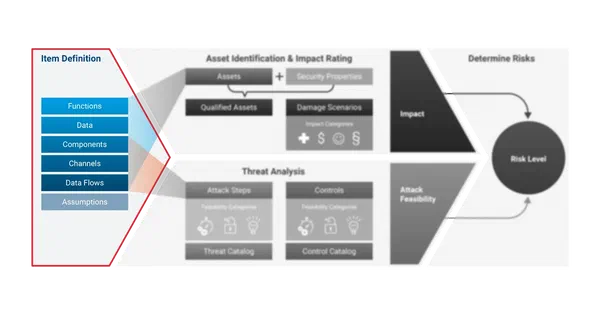
The Item Definition sets the quality ceiling for the whole TARA — what abstraction level is right, why SBOM mapping forces a minimum resolution, and why a living model is the foundation for API and MCP integrations.
Read Article
Jens Bühl
9 min read
Independence is assessed once in a DFA workshop and never revisited. This whitepaper shows how the independence premise in ASIL decompositions can be verified continuously and machine-executed using graph theory.
Download Whitepaper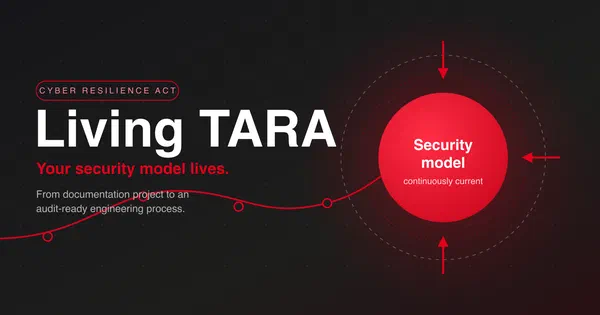
The CRA doesn't ask for a one-time risk analysis — it demands a permanently demonstrable security engineering process. How a Living TARA and the Security Digital Thread keep your risk picture continuously current and audit-ready.
Read Article Dirk Leopold
6 min read
Excel template for CRA risk analysis: TARA in line with ISO/SAE 21434 and IEC 62443 — how to start methodically, what you can import, and when Excel becomes the bottleneck.
Read Article
Jens Bühl
6 min read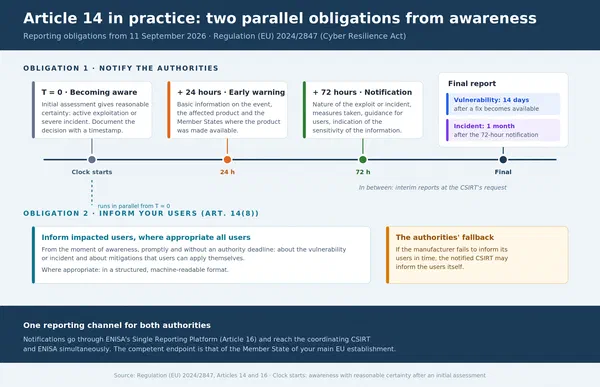
CRA Article 14 reporting obligations take effect on 11 September 2026. This article walks through the complete notification process chronologically — from the initial assessment to the final report — and identifies the points where reporting processes break down in practice.
Read Article
Dirk Leopold
12 min read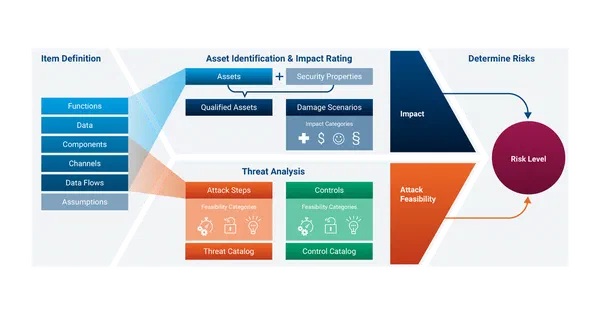
A TARA is not a threat catalogue — it is an auditable record of risk decisions: what it involves, how the process works, and when Excel reaches its limits.
Read Article
Jens Bühl
6 min read
AI can now produce TARAs, traceability matrices, and safety cases that are structurally complete and terminologically correct. That surfaces a question worth asking: what, exactly, is being verified? The problem is not AI-generated documentation. It is compliance processes that optimize for artifacts instead of the properties those artifacts were supposed to encode.
Read Article Florian Antony
6 min read
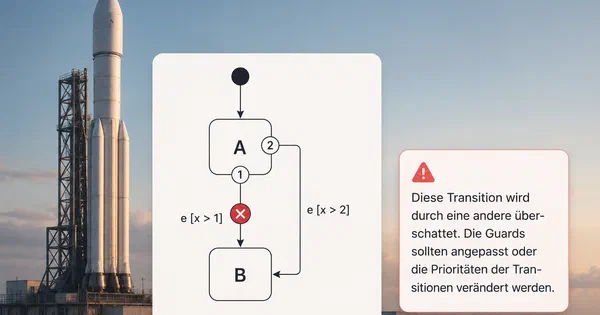
An unreachable transition, an unsatisfiable guard, a numeric overflow: these bugs hide in the model long before any test reveals them. A results report from two master's theses on formal error detection for state machines using symbolic execution and SMT solvers.
Read Article Andreas Mülder
9 min read
How AI assistants reduce TARA creation from weeks to hours — and turn your threat analysis into a real competitive advantage.
Watch Webinar
Jens Bühl
Learn how TARA automation with itemis SECURE (formerly YAKINDU Security Analyst) makes cybersecurity processes in the automotive industry fundamentally more efficient.
Watch Webinar Jonathan Mohring
Forget high-stress assessments with massive teams and mountains of manual documentation. Discover how to make a leap from five weeks to five hours.
Watch Webinar

itemis ANALYZE moves to the cloud — unlocking a new era of Agentic Engineering where your Knowledge Graph becomes the governance layer for your AI.
Watch Webinar

Your TARA is a compliance document. It should be the operational brain of your CSMS. This whitepaper shows how a Living Digital Thread transforms static security artifacts into a continuous, data-driven lifecycle operation.
Download Whitepaper
How leading OEMs and Tier-1 suppliers unite Functional Safety and Cyber Security enterprise-wide — without disrupting proven engineering environments.
Download Whitepaper
Will your product still be legally sellable in Europe after December 2027? This guide shows manufacturers how to approach CRA compliance in 7 structured steps and secure EU market access.
Read Article
Dirk Leopold
5 min read
itemis SECURE is now available on the web — collaborate on cybersecurity projects simultaneously from any device, just like Google Docs.
Watch Webinar
See how itemis CREATE streamlines state machine development and testing in embedded systems — illustrated with a practical Turn Signal Control case study.
Watch Webinar
Axel Terfloth
See how itemis CREATE enables fast statechart development in the cloud, with AI-assisted model generation and seamless Git-based version control.
Watch Webinar
Traceability is more than a compliance checkbox. Learn what it means in software and systems engineering, what insights it unlocks, and what challenges come with it.
Read Article
Florian Antony
5 min read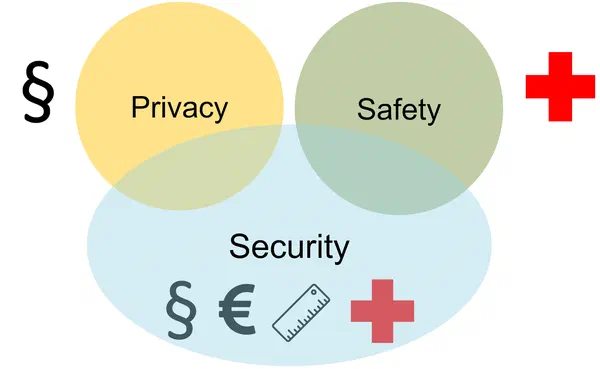
In the automotive domain, security is becoming more and more important – especially for the new generations of connected, (semi-)autonomous vehicles. Learn how to develop a secure system design and which additional security challenges may arise.
Read Article
Dirk Leopold
9 min read
How Franca IDL and itemis CREATE can be integrated to validate embedded software components against interface contracts interactively during development.
Read Article Dr. Klaus Birken
9 min read
How itemis CREATE adds higher-level modeling, simulation and unit testing on top of the SCXML standard.
Read Article
Andreas Mülder
5 min read
In times of Spectre and Meltdown it's totally clear that security is a big engineering challenge. Learn more about safety and security in this post.
Read Article
Dirk Leopold
8 min read
The increased share of software solutions places high demands on Automotive Security. But what changes are coming for the industry and manufacturers?
Read Article
Dirk Leopold
5 min read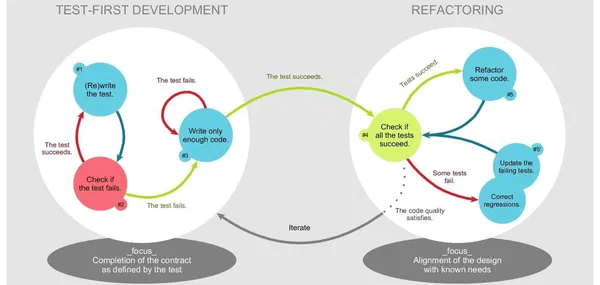
How to apply Test-Driven Development to model-driven software development using SCTUnit, itemis CREATE's unit testing framework for statechart models.
Read Article
Axel Terfloth
6 min read
A requirements traceability matrix is not just a bookkeeping tool. Learn the five key questions it answers in day-to-day project work — plus one bonus question.
Read Article
Florian Antony
6 min read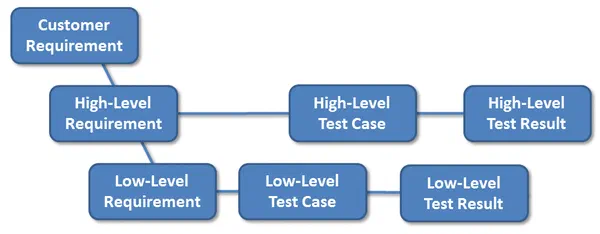
Requirements coverage is demanded by process standards like Automotive SPICE, yet remains poorly defined. Learn what it really means and how to measure it properly.
Read Article
Florian Antony
6 min read
State machines can not only be modeled. In part 5 we present the State Pattern as an implementation variant.
Read Article Rainer Klute
11 min read

Learn how to program an MSP430 microcontroller with state machines using itemis CREATE, fully integrated in Code Composer Studio – with automatic code generation and a graphical editor.
Read Article Robin Herrmann
3 min read
A requirements traceability matrix (RTM) is a simple table that establishes bidirectional traceability across your project. Learn what it is and how to build one in four steps.
Read Article
Florian Antony
5 min read
An empirical study with 71 subjects shows that requirements traceability leads to 24% faster task completion and 50% more correct solutions during software maintenance.
Read Article
Florian Antony
4 min read
State machines can be modeled – but how can they actually be implemented? For example with the help of state tables.
Read Article
Rainer Klute
8 min read
How do modeled state machines become program code? For example with the help of a switch statement. We show how the implementation works.
Read Article
Rainer Klute
6 min read
Learn how to ensure traceability for your itemis CREATE statechart models – with tool support that scales beyond manual trace links.
Read Article
Andreas Mülder
5 min read
In part 2 of the series we cover time-controlled triggering of state transitions, orthogonal regions, and composite states with subdiagrams.
Read Article
Rainer Klute
8 min read
How do state machines work and why should you use them? This post illustrates the modeling of a finite state machine using the example of a blind controller.
Read Article
Rainer Klute
6 min read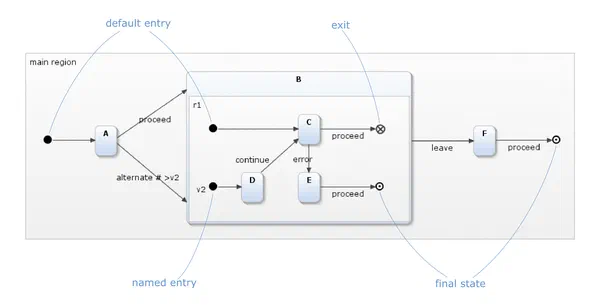
How to use entry points, exit points, and final states in state machine modeling with itemis CREATE.
Read Article
Axel Terfloth
5 min read