Blog
Cyber Security
The TARA Arrives, Its References Don't
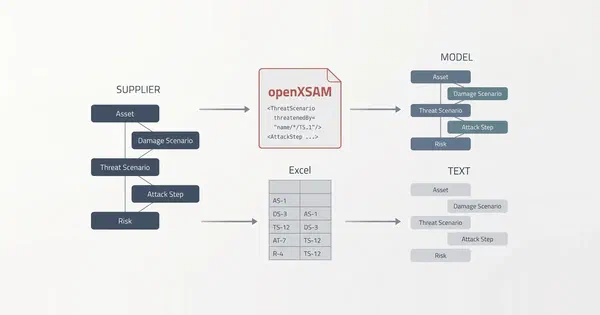
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article Jens Bühl
8 min read
Create individual, consistent threat and risk analyses with minimal effort and adapt them within seconds. Threat modelling and risk assessment – verifiable and efficient – thanks to intelligent AI integration.





itemis SECURE is an AI-powered platform for threat analysis and risk assessment (TARA). It lets you model systems, identify threats and assess cybersecurity risks to ISO/SAE 21434, IEC 62443 and CRA. The results are available as consistent, audit-proof documentation.
Changes to the system can be carried into the analysis within seconds, and AI assistants speed up recurring tasks.
Book a demo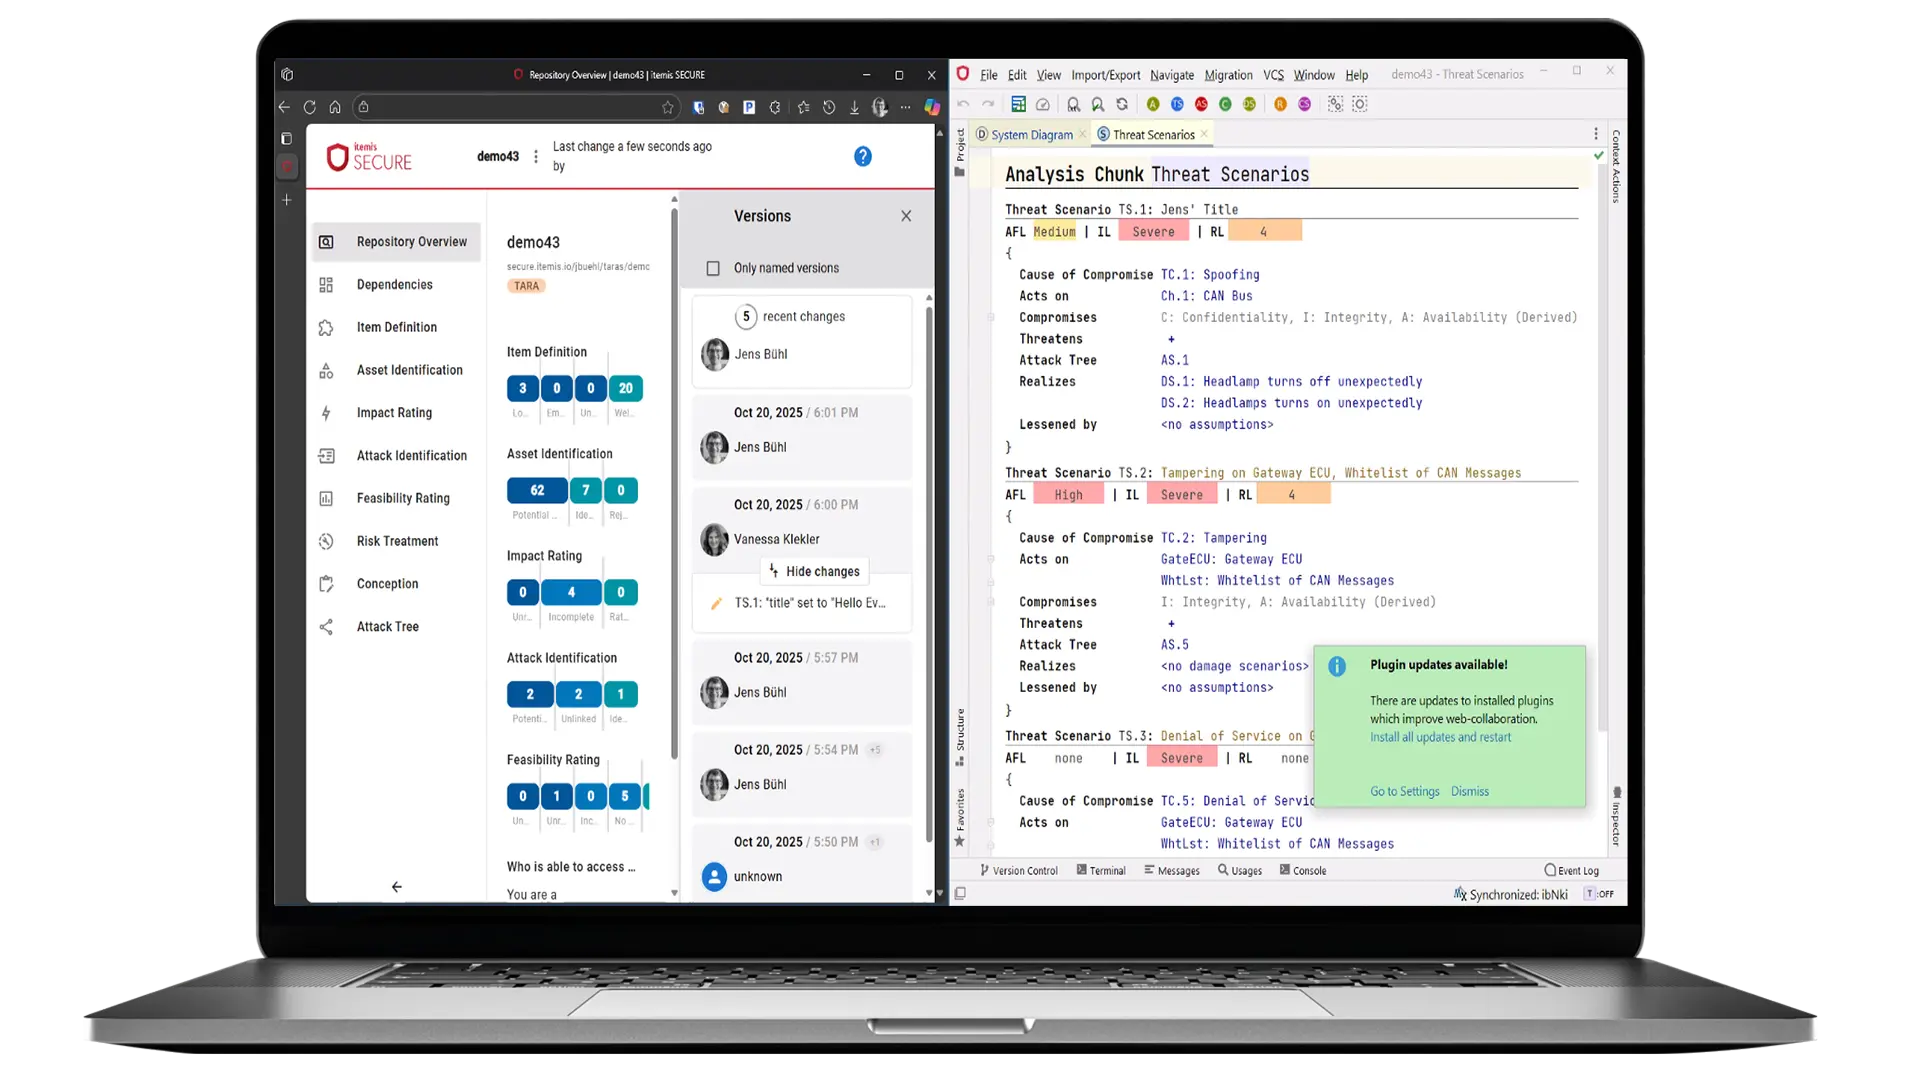
itemis SECURE supports you in meeting the central cybersecurity standards – efficiently, verifiably and at scale.
The automotive industry must demonstrate cybersecurity under ISO/SAE 21434 and UNECE R155. The challenge is time-consuming, fragmented and error-prone manual TARAs across multiple product lines and versions.
IEC 62443 requires translating risk-based cybersecurity requirements into consistent, architecture-driven technical controls for complex industrial systems, while maintaining conformity and documentation.
The EU Cyber Resilience Act demands continuous cybersecurity across the entire product lifecycle: secure-by-design development, vulnerability management and regulatory documentation are all part of it.
DIN CLC/TS 50701 governs cybersecurity in the railway sector and builds on IEC 62443. The challenge is to demonstrate threats and requirements consistently for the zones and conduits of railway-specific systems.
Manufacturers must demonstrate the cybersecurity of medical devices under IEC 81001-5-1 and FDA requirements. This includes a documented threat and risk analysis across the entire product lifecycle.
Your standard is not listed? Methods, assessment models and reports can be adapted to further standards and company-specific requirements. Get in touch, and we will set it up together with you.
The desktop app for threat analysis and risk assessment compliant with ISO/SAE 21434, with interactive attack tree modeling and analysis.
The hybrid approach with real-time collaboration: work on multiple TARAs in parallel and automate collaboration and processes.
Full V model coverage from requirements to start of production, with data from existing systems in a knowledge graph.
Compare the scope of itemis SECURE Classic, Cloud and Lifecycle Integration.
| Feature | itemis SECURE Classic | itemis SECURE Cloud | itemis SECURE Lifecycle Integration |
|---|---|---|---|
| Analysis & modeling | |||
| Threat analysis and risk assessment compliant to ISO/SAE 21434 | |||
| Interactive attack tree modeling and analysis | |||
| Collaboration & automation | |||
| Hybrid approach and real-time collaboration | |||
| Working on multiple TARAs | |||
| Collaboration and automation of processes | |||
| Lifecycle Integration | |||
| Full V model coverage from requirements to start of production | |||
| Integration of data and information from existing systems into a knowledge graph | |||
| Risk-based decision-making considering multiple layers of dependencies | |||
Why a TARA loses its references on the way from supplier to OEM, what openXSAM gets back, and why that takes a model.
Read Article
Jens Bühl
8 min read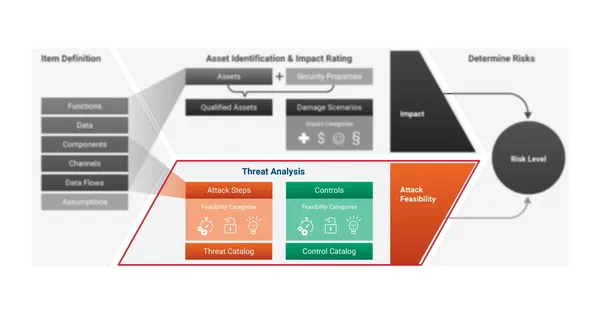
Threat scenario, attack path and attack feasibility belong together: what makes a scenario, why the path gets rated, and how the method shifts the result.
Read Article
Jens Bühl
13 min read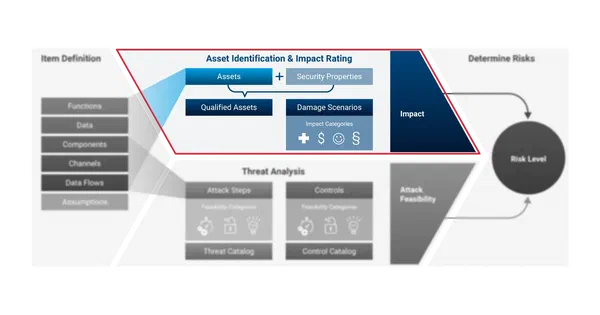
Asset identification and impact rating supply one half of the risk value: when an element of the item becomes an asset, whose damage a damage scenario describes, why the safety rating is not security's to set alone, and what keeps ratings comparable across projects.
Read Article
Jens Bühl
15 min read
The Item Definition sets the quality ceiling for the whole TARA — what abstraction level is right, why SBOM mapping forces a minimum resolution, and why a living model is the foundation for API and MCP integrations.
Read Article
Jens Bühl
9 min read
The CRA doesn't ask for a one-time risk analysis — it demands a permanently demonstrable security engineering process. How a Living TARA and the Security Digital Thread keep your risk picture continuously current and audit-ready.
Read Article Dirk Leopold
6 min read
Excel template for CRA risk analysis: TARA in line with ISO/SAE 21434 and IEC 62443 — how to start methodically, what you can import, and when Excel becomes the bottleneck.
Read Article
Jens Bühl
6 min read